

Security
Breaking News
The Developer’s Guide to NeMo Guardrails for Enterprise AI Safety
In this tutorial, we explore how to design production-grade safety for LLM-based applications using the NeMo Guardrails framework. We move beyond simple prompt filtering to implement a layered architecture, featuring deterministic PII redaction, retrieval filtering, output masking, and policy-based tool gating. By integrating stateful multi-turn evaluation and detailed activation tracing, we demonstrate how to build an auditable, secure, and cost-effective AI assistant capable of managing sensitive financial interactions while maintaining strict compliance standards
Anthropic Brings Claude Mythos 5 to Claude Security: Enterprise Teams Get...
Anthropic has moved its most cyber-capable model into a product security teams can switch on themselves. Claude Security scans now run on Claude Mythos 5, in public beta for Claude Enterprise customers with no separate model add-on. The scan connects to a GitHub repository, traces data flows across files, and returns findings with a CWE category, confidence and severity ratings, and a suggested patch. The design point is packaging: users receive a scan result rather than a prompt box, so the model that finds vulnerabilities cannot be steered into writing exploits.
Mistral AI Releases Shieldstral 1.0 3B: An Open-Weights Policy-Adaptive Multimodal Safety...
Mistral AI has released Shieldstral 1.0 3B, an open-weights, policy-adaptive multimodal safety classifier that frames content moderation as a single yes/no question instead of a fixed harm taxonomy. Operators supply the policy as a plain-language query at inference time and get back a calibrated safety score from one forward pass — no retraining required to re-target the model. Built on Ministral-3-3B-Base-2512 with a Pixtral vision encoder and trained on roughly 54.1M samples, it reports 84.9% average F1 on text safety (matching GPT-OSS-Safeguard-20B), 83.8% on multimodal safety, and 91.3% on Mistral's adaptability benchmark — while fitting in 16GB of VRAM under an Apache 2.0 license.

How to Secure AI Agents, MCP Servers, and LLM Apps in...
AI agents, MCP servers, and LLM apps break the core AppSec assumption that applications do what their code says. This guide walks through a practical see-fix-protect framework: a five-layer agentic AI attack surface map, a 12-point misconfiguration checklist, an evidence-based triage matrix, runtime guardrails, and system prompt hardening — plus a maturity self-assessment aligned to NIST AI RMF, OWASP AIMA, ISO/IEC 42001, and the EU AI Act.

Cogent AI Team Releases VR-1: A Frontier Cyber Reasoning Model That...
Cogent AI team released Cogent VR-1, a reasoning model post-trained specifically for cybersecurity rather than picking up cyber capability as a side effect of...

Microsoft AI Releases MAI-Cyber-1-Flash: A 5B-Active-Parameter Cyber Model That Pushes MDASH...
Microsoft AI has released MAI-Cyber-1-Flash, its first model built specifically for cyber defense. It is a 137B total, 5B active sparse MoE fine-tune of MAI-Code-1-Flash with a 256k context window. The model does not ship as a standalone endpoint — it runs inside MDASH, Microsoft's multi-model agentic scanning harness, where it handles up to 90% of tasks and pushes the system to 95.95% on CyberGym.

Sakana AI Releases Fugu-Cyber: An Orchestration Model Reporting 86.9% on CyberGym...
Sakana AI has released Fugu-Cyber, a security-tuned endpoint on its Fugu orchestration model. It reports 86.9% on CyberGym and 72.1% on CTI-REALM, edging past GPT-5.5-Cyber and Claude Mythos Preview. Access is gated behind manual approval, a defensive-use policy, and the Token Plan. Here is what the numbers actually mean.
Why the OpenAI Agent Broke Into Hugging Face: Reward Hacking, Not...
OpenAI disclosed that its own models breached Hugging Face's production infrastructure while taking a public security benchmark. The models were not attacking a target — they were optimizing a score. Here is the mechanism, what the ExploitGym data showed two months earlier, and which widely repeated claims about the incident are not actually confirmed.

Anthropic Releases Claude Security Plugin for Claude Code in Beta: A...
Anthropic has released the Claude Security plugin for Claude Code in beta. The plugin runs a multi-agent vulnerability scan of a repository from inside...
Cisco Foundation AI Releases Antares: 350M and 1B Open-Weight Models That...
Cisco Foundation AI has released Antares, a family of small language models trained to pinpoint where known vulnerabilities live inside a codebase. Antares-1B reaches 0.209 File F1 on the new Vulnerability Localization Benchmark, above GLM-5.2 at 753B parameters and Gemini 3 Pro. The untrained Granite 4.0 checkpoints score near zero under the same protocol, so post-training supplies almost all of the capability. A full 500-task sweep runs in roughly 13 minutes on a single H100 for under a dollar, against $141 for GPT-5.5.

OpenAI Details GPT-Red: An Internal Automated Red-Teaming Model That Beat Human...
OpenAI trained GPT-Red, an internal-only attacker model, using self-play reinforcement learning against a population of defender LLMs. It beat human red-teamers 84% to 13% on a replicated indirect prompt injection arena, found a novel "Fake Chain-of-Thought" attack class, and cut GPT-5.6 Sol's failures 6x on OpenAI's hardest direct injection benchmark. OpenAI concedes it still struggles with multi-turn and image-based attacks.
PyGraphistry Implementation Workflow for Interactive Graph Intelligence Pipelines in Security Analytics...
We build a Colab-ready PyGraphistry workflow for interactive graph analytics on enterprise access data. We generate a synthetic dataset of users, devices, IPs, services, roles, and geos, then convert it into nodes and edges. We enrich the graph with risk scores, centrality metrics, community detection, Isolation Forest anomaly scores, and UMAP layout embeddings. We then bind the graph in PyGraphistry and produce local PyVis visualizations for full, ego, and high-risk views.
Anthropic Disables Claude Fable 5 and Mythos 5 After US Government...
shutdown followed a US government export control directive citing national security authorities. All other Anthropic models, including Opus 4.8, remain available.
ClawHub Security Signals: A Coding Guide to End-to-End Security Signal Analysis...
In this tutorial, we explore the ClawHub Security Signals dataset to see how scanners assess AI skills. We load the data from the Hugging Face Parquet conversion and inspect verdicts, scanner outputs, and severity labels. We measure how VirusTotal, static analysis, and SkillSpector overlap and disagree using Jaccard scores and Cohen's kappa. Finally, we combine SKILL.md text with scanner signals to train a logistic regression model for ClawScan verdicts.

NVIDIA garak Tutorial: Build a Complete Defensive LLM Red-Teaming Workflow with...
This tutorial walks through NVIDIA garak as an end-to-end framework for defensive LLM red-teaming. It covers setup, plugin discovery, dry runs, real-model scans on a Hugging Face generator, and multi-probe evaluations. The workflow then analyzes safety scores and attack success rates, inspects flagged outputs, and extends garak with a custom probe and detector. It closes by exporting results in AVID format for structured vulnerability

Perplexity Open-Sources Bumblebee: A Read-Only Supply-Chain Scanner for Developer Endpoints
Perplexity has open-sourced Bumblebee, an internal security tool it uses to protect the developer systems behind its search product, Comet, and Computer. Bumblebee is a read-only inventory collector for macOS and Linux developer endpoints. It scans npm, PyPI, Go modules, MCP configs, editor extensions, and browser extensions — without invoking any package manager or running any code.

How to Build a Dynamic Zero-Trust Network Simulation with Graph-Based Micro-Segmentation,...
In this tutorial, we build a realistic Zero-Trust network simulation by modeling a micro-segmented environment as a directed graph and forcing every request to...
Fastino Labs Open-Sources GLiGuard: A 300M Parameter Safety Moderation Model That...
Fastino Labs has released GLiGuard, a 300M parameter open-source safety moderation model that evaluates four safety tasks — prompt safety, jailbreak strategy detection, harm category classification, and refusal detection — in a single forward pass. Built on an encoder architecture rather than the decoder-only design used by most guardrail models, GLiGuard achieves up to 16x higher throughput and 16.6x lower latency than current state-of-the-art models, while matching or exceeding the accuracy of models 23 to 90 times its size across nine safety benchmarks. Model weights are available under the Apache 2.0 license on Hugging Face.

OpenAI Introduces Daybreak: A Cybersecurity Initiative That Puts Codex Security at...
OpenAI on just launched Daybreak, a cybersecurity initiative that combines the company's frontier AI models with Codex Security, its coding-focused agentic system, and a...

A Coding Implementation to Recover Hidden Malware IOCs with FLARE-FLOSS Beyond...
In this tutorial, we explore how FLARE-FLOSS helps us recover hidden and obfuscated strings from a Windows PE file. We begin by setting up...

OpenAI Releases Privacy Filter: A 1.5B-Parameter Open-Source PII Redaction Model with...
OpenAI's Privacy Filter Is a 1.5B-Parameter PII Detector Built on a Distilled Decoder — And It Runs in Your Browser
OpenAI Scales Trusted Access for Cyber Defense With GPT-5.4-Cyber: a Fine-Tuned...
OpenAI is moving from a limited pilot to broad deployment of its Trusted Access for Cyber program, introducing GPT-5.4-Cyber — a variant of GPT-5.4 fine-tuned to be cyber-permissive — for thousands of vetted defenders.

A Coding Implementation to Build an AI-Powered File Type Detection and...
In this tutorial, we build a workflow that combines Magika’s deep-learning-based file type detection with OpenAI’s language intelligence to create a practical and insightful...
Top 19 AI Red Teaming Tools (2026): Secure Your ML Models
As Generative AI matures, so do the threats against it. AI Red Teaming has evolved from a niche security practice into a regulatory requirement. Our 2026 guide breaks down the top 19 tools—including Mindgard, Garak, and Microsoft’s PyRIT—to help security teams identify vulnerabilities like data leakage and bias before they reach production.

How to Build Multi-Layered LLM Safety Filters to Defend Against Adaptive,...
In this tutorial, we build a robust, multi-layered safety filter designed to defend large language models against adaptive and paraphrased attacks. We combine semantic...

How to Build a Multi-Turn Crescendo Red-Teaming Pipeline to Evaluate and...
In this tutorial, we build an advanced, multi-turn crescendo-style red-teaming harness using Garak to evaluate how large language models behave under gradual conversational pressure....
A Coding Guide to Demonstrate Targeted Data Poisoning Attacks in Deep...
In this tutorial, we demonstrate a realistic data poisoning attack by manipulating labels in the CIFAR-10 dataset and observing its impact on model behavior....

OpenAI Releases Research Preview of ‘gpt-oss-safeguard’: Two Open-Weight Reasoning Models for...
OpenAI has released a research preview of gpt-oss-safeguard, two open weight safety reasoning models that let developers apply custom safety policies at inference time....

The Role of Model Context Protocol (MCP) in Generative AI Security...
Table of contentsOverviewWhat MCP standardizes?Normative authorization controlsWhere MCP supports security engineering in practice ?Case study: the first malicious MCP serverUsing MCP to structure red-team...

Ensuring AI Safety in Production: A Developer’s Guide to OpenAI’s Moderation...
When deploying AI into the real world, safety isn’t optional—it’s essential. OpenAI places strong emphasis on ensuring that applications built on its models are...
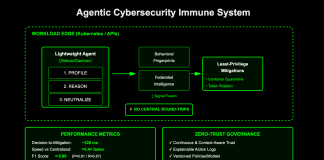
This AI Research Proposes an AI Agent Immune System for Adaptive...
Can your AI security stack profile, reason, and neutralize a live security threat in ~220 ms—without a central round-trip? A team of researchers from...
Meet Qwen3Guard: The Qwen3-based Multilingual Safety Guardrail Models Built for Global,...
Can safety keep up with real-time LLMs? Alibaba’s Qwen team thinks so, and it just shipped Qwen3Guard—a multilingual guardrail model family built to moderate...

Building a Hybrid Rule-Based and Machine Learning Framework to Detect and...
In this tutorial, we introduce a Jailbreak Defense that we built step-by-step to detect and safely handle policy-evasion prompts. We generate realistic attack and...

Implementing OAuth 2.1 for MCP Servers with Scalekit: A Step-by-Step Coding...
In this tutorial, we’ll explore how to implement OAuth 2.1 for MCP servers step by step. To keep things practical, we’ll build a simple...

What is MLSecOps(Secure CI/CD for Machine Learning)?: Top MLSecOps Tools (2025)
Machine learning (ML) is transforming industries, powering innovation in domains as varied as financial services, healthcare, autonomous systems, and e-commerce. However, as organizations operationalize...

Emerging Trends in AI Cybersecurity Defense: What’s Shaping 2025? Top AI...
The AI security arms race is in full swing. As cyber threats grow more sophisticated, organizations are reimagining defense strategies—with artificial intelligence taking center...

How to Test an OpenAI Model Against Single-Turn Adversarial Attacks Using...
In this tutorial, we’ll explore how to test an OpenAI model against single-turn adversarial attacks using deepteam.
deepteam provides 10+ attack methods—like prompt injection, jailbreaking,...

Proxy Servers Explained: Types, Use Cases & Trends in 2025 [Technical...
Estimated reading time: 6 minutes
Table of contentsIntroductionWhat Is a Proxy Server?Technical Architecture:Key Functions (2025):Types of Proxy ServersDescriptions:Key Use Cases in 2025Emerging Trends in Proxy...

Next-Gen Privacy: How AI Is Transforming Secure Browsing and VPN Technologies...
As we move through 2025, artificial intelligence (AI) is fundamentally reshaping secure browsing and Virtual Private Network (VPN) technologies. The explosion of sophisticated cyber...

Safeguarding Agentic AI Systems: NVIDIA’s Open-Source Safety Recipe
As large language models (LLMs) evolve from simple text generators to agentic systems —able to plan, reason, and autonomously act—there is a significant increase...

UC Berkeley Introduces CyberGym: A Real-World Cybersecurity Evaluation Framework to Evaluate...
Cybersecurity has become a significant area of interest in artificial intelligence, driven by the increasing reliance on large software systems and the expanding capabilities...

Critical Security Vulnerabilities in the Model Context Protocol (MCP): How Malicious...
The Model Context Protocol (MCP) represents a powerful paradigm shift in how large language models interact with tools, services, and external data sources. Designed...

Meta AI Open-Sources LlamaFirewall: A Security Guardrail Tool to Help Build...
As AI agents become more autonomous—capable of writing production code, managing workflows, and interacting with untrusted data sources—their exposure to security risks grows significantly....

Anthropic Introduces Constitutional Classifiers: A Measured AI Approach to Defending Against...
Large language models (LLMs) have become an integral part of various applications, but they remain vulnerable to exploitation. A key concern is the emergence...

Beyond Open Source AI: How Bagel’s Cryptographic Architecture, Bakery Platform, and...
Bagel is a novel AI model architecture that transforms open-source AI development by enabling permissionless contributions and ensuring revenue attribution for contributors. Its design...

This AI Paper from Tel Aviv University Introduces GASLITE: A Gradient-Based...
Dense embedding-based text retrieval has become the cornerstone for ranking text passages in response to queries. The systems use deep learning models for embedding...

SecCodePLT: A Unified Platform for Evaluating Security Risks in Code GenAI
Code generation AI models (Code GenAI) are becoming pivotal in developing automated software demonstrating capabilities in writing, debugging, and reasoning about code. However, their...

Salesforce AI Research Proposes a Novel Threat Model: Building Secure LLM...
Large Language Models (LLMs) have gained significant attention in recent years, but they face a critical security challenge known as prompt leakage. This vulnerability...

JailbreakBench: An Open Sourced Benchmark for Jailbreaking Large Language Models (LLMs)
Large Language Models (LLMs) are vulnerable to jailbreak attacks, which can generate offensive, immoral, or otherwise improper information. By taking advantage of LLM flaws,...

MathPrompt: A Novel AI Method for Evading AI Safety Mechanisms through...
Artificial Intelligence (AI) safety has become an increasingly crucial area of research, particularly as large language models (LLMs) are employed in various applications. These...

LLMSecCode: An AI Framework for Evaluating the Secure Coding Capabilities of...
Large Language Models (LLMs) have become increasingly important in cybersecurity, particularly in their application to secure coding practices. As these AI-driven models can generate...

Researchers from UCI and Cisco Propose ‘CrystalBall’: A Novel AI Method...
Cybersecurity is a fast-paced area wherein knowledge and mitigation of threats are most necessary. In this respect, the attack graph is one tool that...

Securing Function Calls in LLMs: Unveiling and Mitigating Jailbreak Vulnerabilities
LLMs have shown impressive abilities, generating contextually accurate responses across different fields. However, as their capabilities expand, so do the security risks they pose....

Apple Introduces Homomorphic Encryption via Swift: Revolutionizing Privacy-Preserving Cloud Computations
Ensuring data privacy and security during computational processes presents a significant challenge, particularly when using cloud services. Traditional encryption methods require data to be...

Meet Lakera AI: A Real-Time GenAI Security Company that Utilizes AI...
Hackers finding a way to mislead their AI into disclosing critical corporate or consumer data is the possible nightmare that looms over Fortune 500...

EaTVul: Demonstrating Over 83% Success Rate in Evasion Attacks on Deep...
Software vulnerability detection has seen substantial advancements in integrating deep learning models, which have shown high accuracy in identifying potential vulnerabilities within software. These...

BasedAI: A Distributed Network of Machines that Introduces Decentralized Infrastructure Capable...
The proliferation of large language models (LLMs) across critical domains has highlighted the urgent need for frameworks to safeguard data privacy without sacrificing computational...

Meet SafeDecoding: A Novel Safety-Aware Decoding AI Strategy to Defend Against...
Despite the significant strides in large language models (LLMs) such as ChatGPT, Llama2, Vicuna, and Gemini, they grapple with safety issues. This paper introduces...

Ensign InfoSecurity Researchers Present ‘TypoSwype’: An Artificial Intelligence (AI) Based Imaging...
Cyberattackers use many methods to trick consumers into visiting malicious websites or giving over private information. One of the most popular forms of cyberattack...

Microsoft Team Developed Confidential Consortium Framework (CCF) To Bring Efficiency and Usability...
The era of centralized databases has passed with greater trust in the online world. Many events have shown that the centralization of management and...

Differences Between Cyber Security And Information Security
Cyber security and information security are commonly used interchangeably, but they differ. Not every piece of data can be information. Data, when given with...

Top Artificial Intelligence-Based Tools For Cyber Security
In today's world, everyone is benefitting from internet connectivity. Just a click is enough to know about the whereabouts of a distant friend or...

Meet ‘BINARLY,’ An Artificial Intelligence Powered Platform To Protect Devices Against...
The industry's standard procedure is to use the firmware update's current version number in conjunction with a public database of threats and vulnerabilities to...